INFORMED DECISIONS · STRONGER SECURITY
ASSESSMENTS &
EVALUATIONS
— DOCUMENTED BASIS
— INFORMED DECISIONS
— DEFENSIBLE RESULTS
Praesidium develops and evaluates security program documentation that translates regulatory requirements, facility-specific analyses, and operating experience into practical, defensible security measures. The objective is to establish a clear technical and regulatory basis for how protection requirements are defined, implemented, demonstrated, and maintained.
Our assessments integrate program documentation with the physical and operational characteristics of the facility. This approach helps ensure that security requirements remain traceable to their source, implementation activities are aligned with major project milestones, and vulnerabilities are evaluated within the context of the actual Physical Protection System.
The result is a structured framework for program development, phased implementation, requirements traceability, and vulnerability assessment throughout the facility lifecycle.
01
SECURITY
PLANS
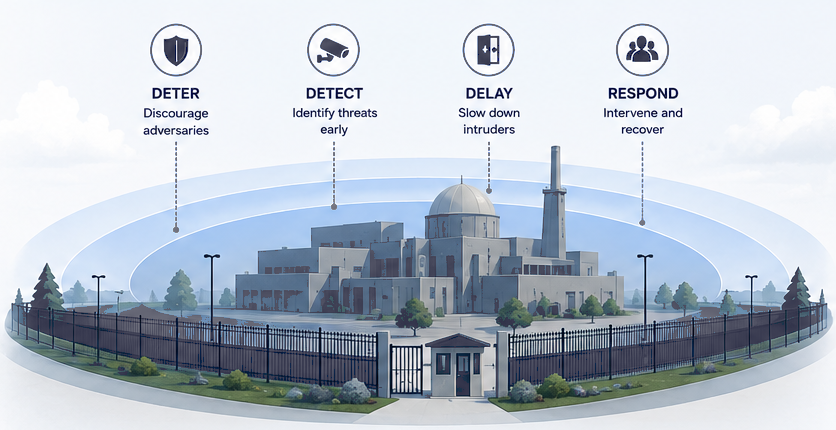
Develop integrated security program documentation, including Physical Security Plans, Contingency Response Plans, and Training and Qualification Plans. Plans translate regulatory requirements and facility-specific security objectives into clear, implementable measures for protecting personnel, assets, and critical functions.
Clear, integrated plans translate security requirements into executable program direction.
02
SECURITY IMPLEMENTATION
ROADMAPS
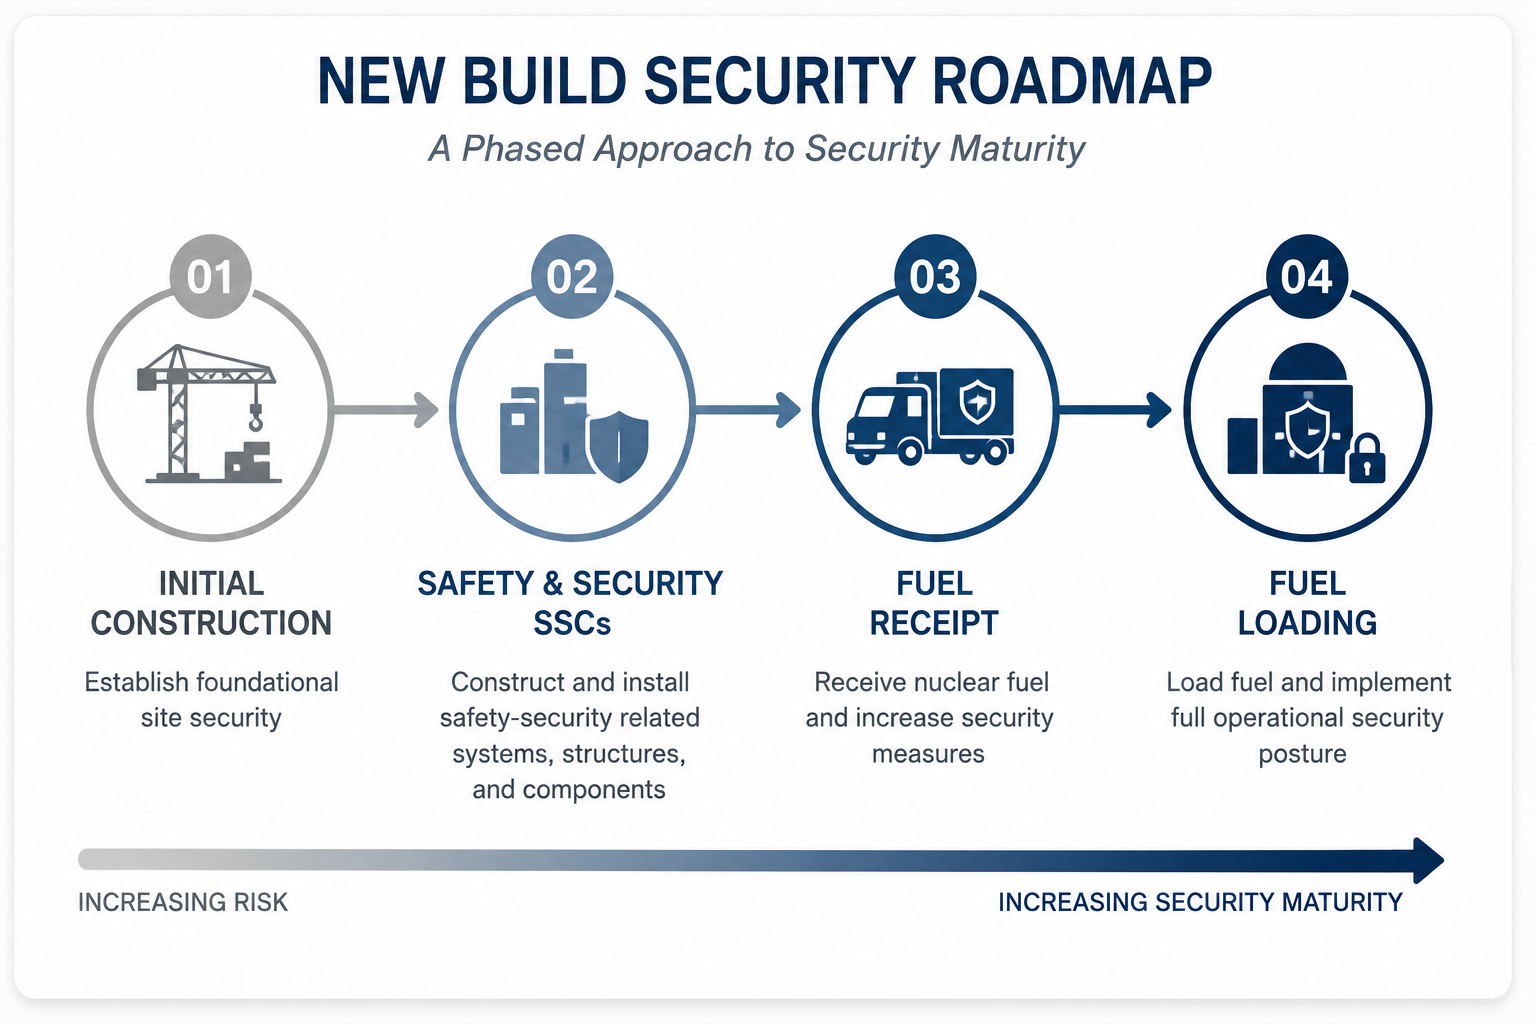
Develop phased security roadmaps that align protection requirements with major project milestones, including construction, fuel receipt, and fuel loading. Roadmaps establish when security measures must be implemented, identify dependencies between security and facility development, and help avoid unnecessary cost or schedule impacts while maintaining regulatory readiness.
A phased roadmap aligns security readiness with the milestones that change facility risk and regulatory posture.
03
REQUIREMENTS TRACE
MATRICES
Develop structured traceability matrices connecting regulatory requirements, site-specific analyses, and relevant operating experience to facility security measures and program documentation. The matrices provide a defensible basis for demonstrating how individual requirements are addressed while identifying gaps, overlaps, and areas requiring further evaluation.
Traceability provides a transparent, auditable basis showing how each requirement is addressed.
04
VULNERABILITY
ASSESSMENTS
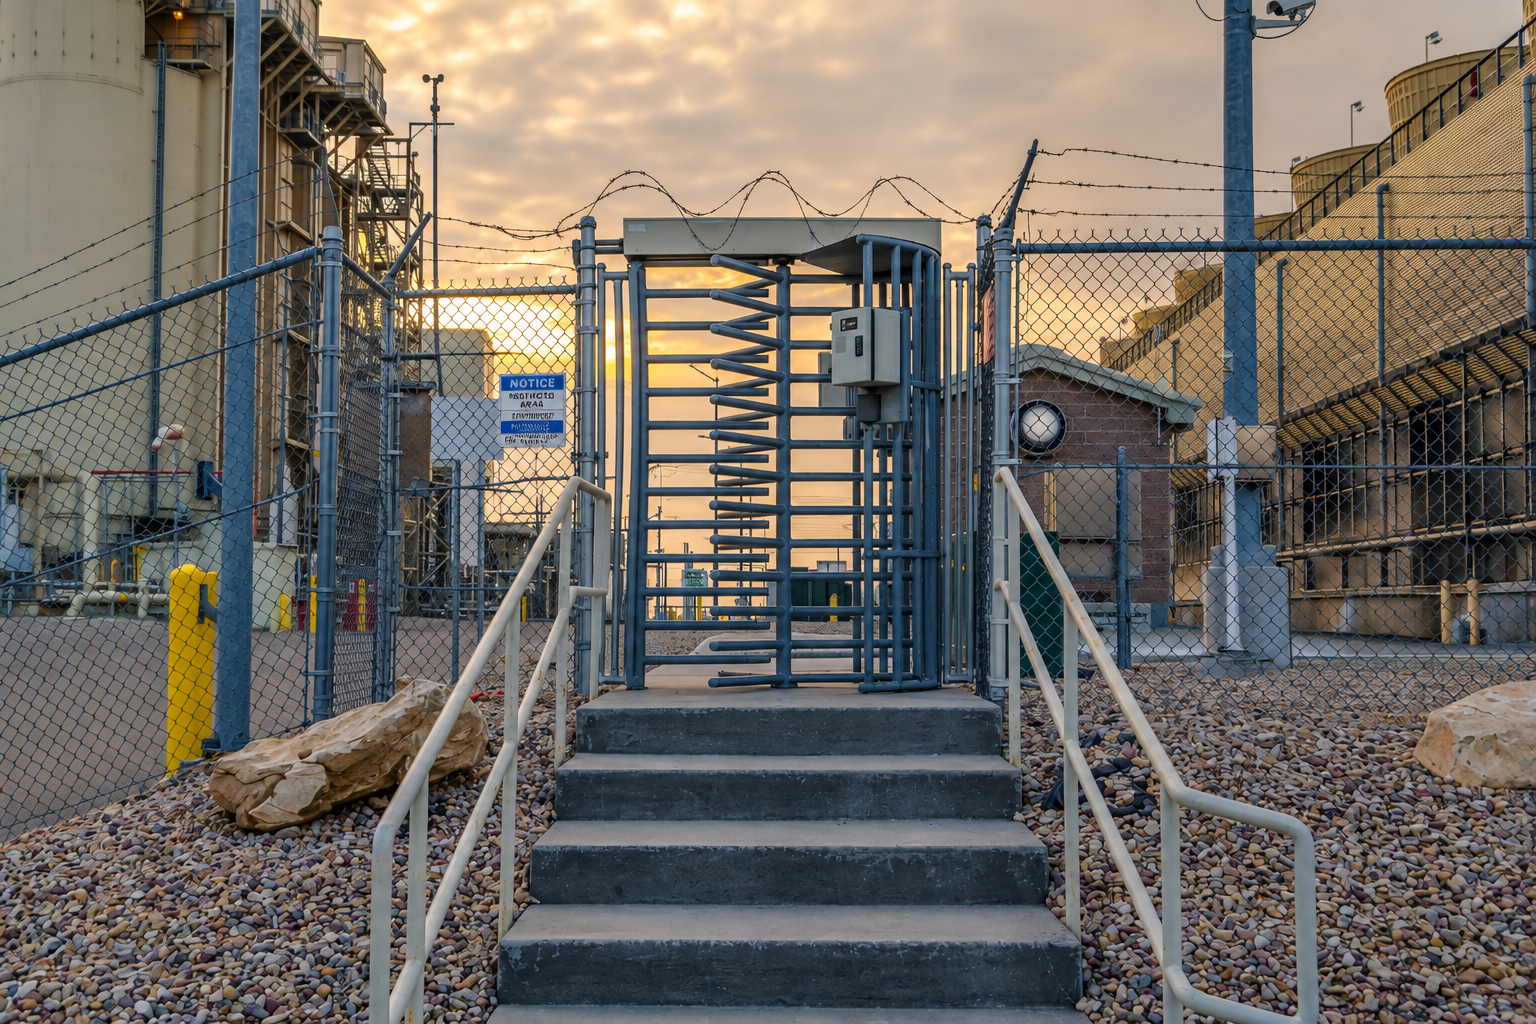
Perform systematic vulnerability assessments integrating facility characteristics, target sets, and the attributes of the Design Basis Threat. Assessments integrate detailed analytical inputs—including pathway analysis where appropriate—with detection and delay capabilities, response effectiveness, and opportunities for exploitation to determine whether the Physical Protection System provides effective and balanced protection.
The assessment establishes whether the integrated protection system can interrupt credible adversary pathways and protect required assets.